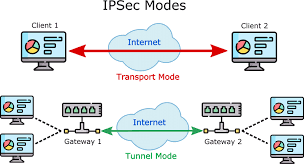
The main difference between Transport Mode and Tunnel Mode is how they protect IP packets during transmission.
Transport Mode
Encrypts only the data (payload) of the IP packet.
The original IP header remains visible, allowing routers to forward the packet normally.
It is commonly used for host-to-host communication, where both devices support IPsec directly.
Since only the payload is encrypted, it has lower overhead and better performance.
Tunnel Mode
Encrypts the entire original IP packet, including the header, and then adds a new IP header.
This provides a higher level of security because the original source and destination addresses are hidden.
It is widely used for site-to-site VPNs and remote-access VPNs, where secure communication between different networks is required.
The additional encapsulation creates slightly more overhead but offers stronger protection.
In simple terms:
Transport Mode = Protects only the data.
Tunnel Mode = Protects the entire packet by encapsulating it inside a new packet.
If you're securing communication between two individual computers, Transport Mode is usually sufficient. If you're connecting entire networks over the internet through a VPN, Tunnel Mode is the preferred choice because it encrypts the complete packet and hides the internal network information.